Documents
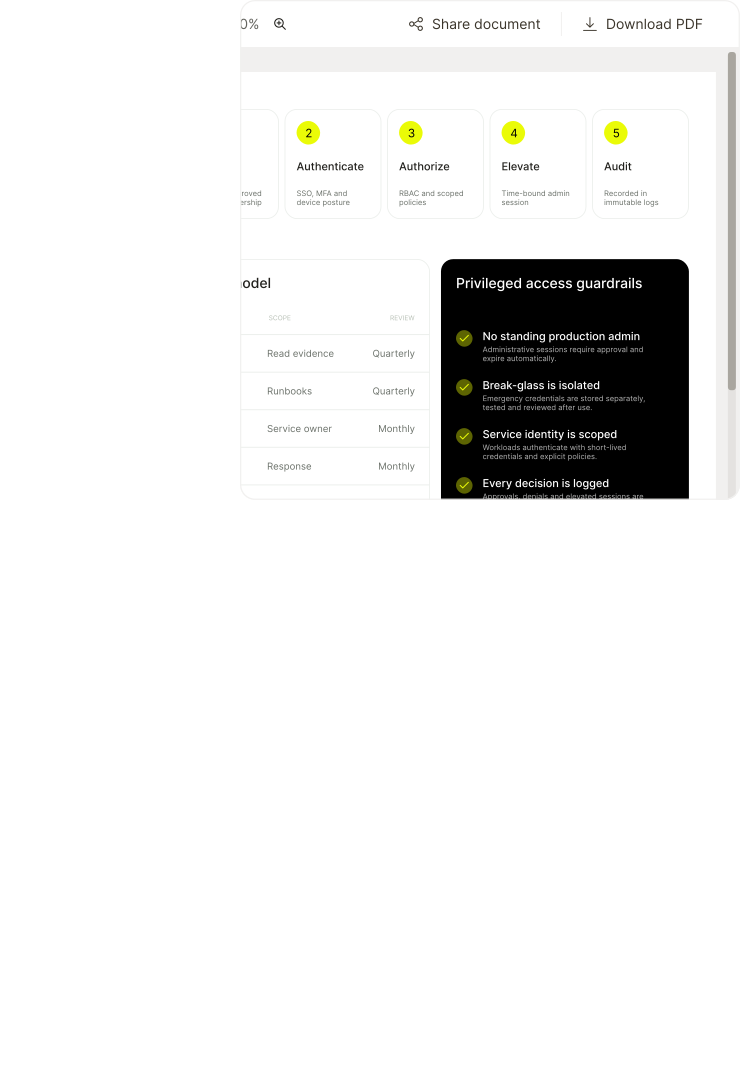
Share SOC2,ISO, pentest and other reports in a structured, access-controlled library.

Give prospects a clear place to request access, sign the appropriate NDA, and download watermarked documents while your teamins control.
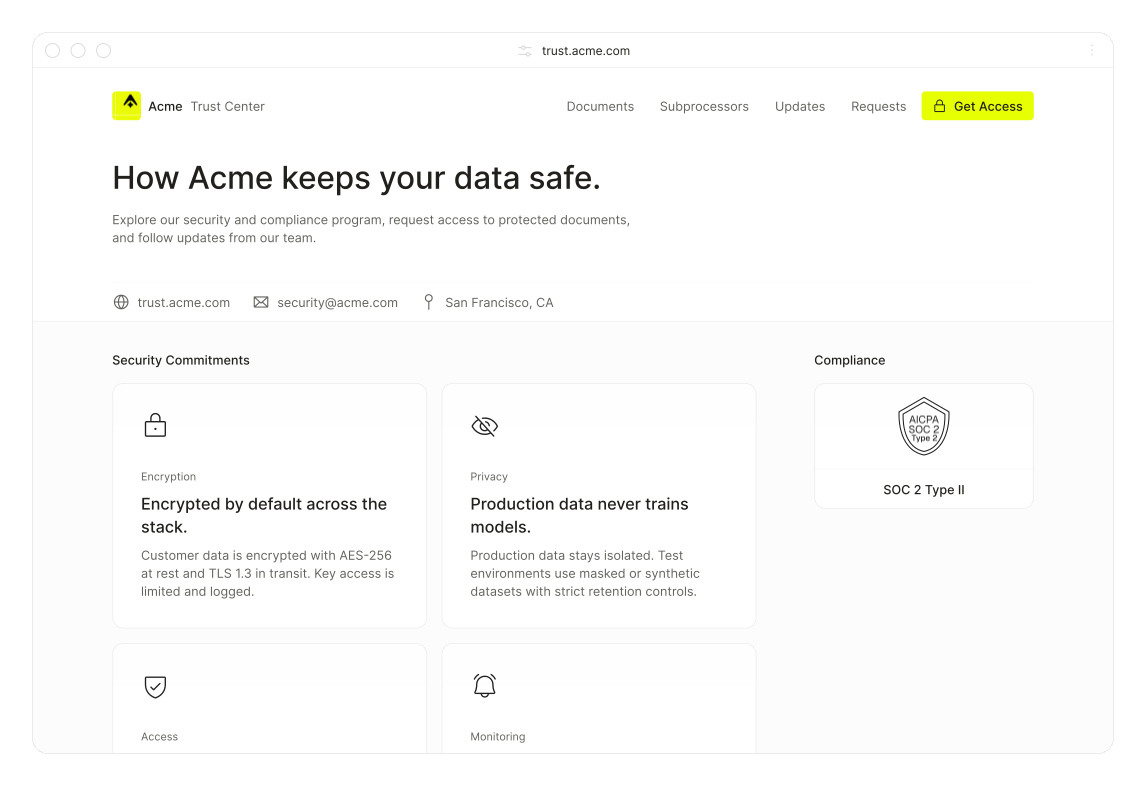
Help buyers find the right materials faster, while your team decides what is public, restricted, or only approved.
Share key security materials from a single Compliance Portal and decide what remains public, restricted, or only approved.
Review access requests in Slack and keep rules aligned with how your team already works.
Allow prospects to sign a NDA in the compliance portal before downloading protected, watermarked files.
Allow prospects to connect with SSO or magic links without creating another account.
Choose which policy, subprocessor, report, or audit updates subscribers should receive.
Approve requests in Slack, support SSOs or magic links, and keep each permission attached to the right company.
Organize policies, controls, reports, audits and suppliers into clear categories, instead of scattered compliance materials.
Share SOC2,ISO, pentest and other reports in a structured, access-controlled library.
Allow buyers to open, review and download each PDF in a secure and focused experience.
Provide buyers with the audit history and historical compliance materials they need when appropriate.
List of subprocessors with the context in which buyers need to assess risk.
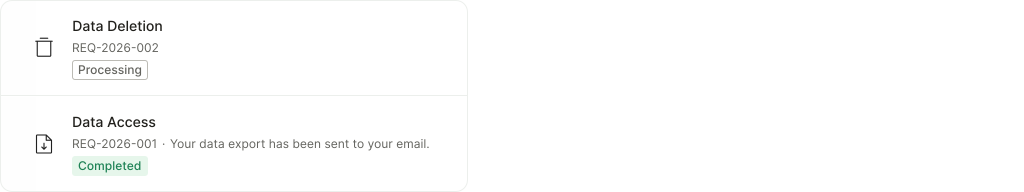
Manage customer data requests through a guided flow, from identity verification to delivery to export.
Explain what your company is committed to security in a concise, scanable and engaging format.
Security teams use ZebraByteto share the right materials, protect sensitive documents, and keep access requests moving.
“ZebraBytes has occupied the SOC2 and compliance so we can focus on construction.”

Reference teams and compliance-ready workflows



Can’t find the framework you are looking for?
Talk to us — we may be able to include it in the program.
Don’t see the framework you are looking for?
Reach out – it may already be supported in the program.