What are the steps towards compliance?
Navigating business compliance is an overwhelming but essential challenge for start-ups as adhering to standards like the GDPR. SOC 2, andISO27001 is essential for building customer trust and ensuring enterprise business. Manual management of these requirements is often a chaotic, resource drainage process that draws engineers away from product development and risks costly errors or lost deadlines. The key is to move from a reactive approach to a proactive one by building a clear, step-by-step technical roadmap that turns compliance from a source of stress into a manageable project.
Key Takeaways
- Compliance is a motor of growth: For start-ups, obtaining compliance with frameworks such as GDPR, SOC 2, orISO27001 is a strategic necessity.It is the key to unlocking the business of the enterprise, meeting legal requirements and building the fundamental trust needed to win customers.
- A Tailored Roadmap is a Must: Avoid generic, one-size-fits-all templatesThe right approach is a customized program built for your specific business and technology, which involves assessing unique risks, creating relevant documents, and implementing controls that really matter.
- The expert guide releases your team: Manual compliance management can be a significant leakage of a startup’s most valuable resource: its engineering team. Partnership with compliance experts turns the process from a complex internal task to a managed journey, allowing your team to stay focused on building your product.
If an expert-led approach is right for you, the platform is here to manage this journey.
Why Compliance is Critical for Your Startup
Before building a roadmap, it’s essential to understand the core business factors behind compliance. For a startup, it’s not just about following the rules; it’s a strategic imperative for growth and survival.
- It unlocks enterprise deals. Many large companies do not want or can do business with suppliers that do not have security certifications, such as: SOC 2 Compliance is often a non-contractual prerequisite for obtaining past security assessments and concluding high-value contracts.
- It’s a legal requirement. Depending on your industry and where your customers are located, compliance is not optional. Regulations like GDPR and HIPAA pose the risk of severe financial penalties that can be devastating for a company in its early stages.
- It builds foundational trust. Compliance is a powerful way to demonstrate that you take data protection seriously, building the essential trust needed for users to adopt your product.
- It creates a competitive advantage. In a competitive market, the ability to demonstrate your security position can distinguish you.It signals maturity and stability to investors and customers, giving you an advantage over less trained competitors.
Build your compliance roadmap
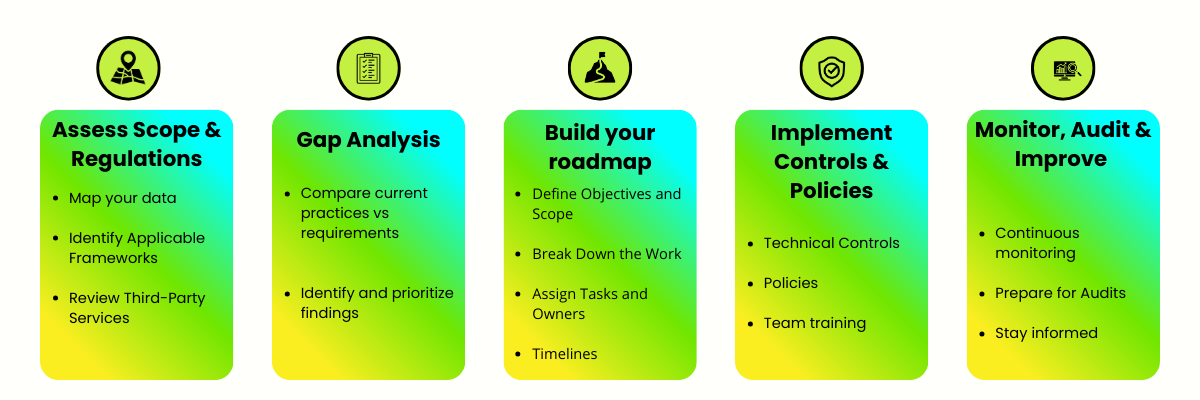
Here is a practical step-by-step guide to creating your compliance roadmap.
Step 1: Evaluate scope and identify regulations
Before you can build a plan, you need to understand the landscape.
- Map Your Data: Identify and categorize all data that your products collect, process and store. Pay special attention to personal or sensitive data.
- Identify Applicable Frameworks: Based on the market, industry and data types, determine which regulations apply to your business. SOC 2, HIPAA, or others.
- Review Third-Party Services: You are responsible for their compliance so that you ensure that they meet the required standards.
Step 2: Conduct a Gap Analysis
With a clear understanding of the requirements, you can now evaluate your current posture.
- Review Current Practices: Compare existing policies, procedures and technical controls with the specific regulatory requirements you have identified.
- Document the Gaps: Create a detailed list of each area where your current practices do not meet compliance requirements.
- Prioritize Findings: Not all gaps are equal. Prioritize them based on the level of risk and the effort needed to fix them. High-risk areas such as data encryption and access control should be at the top of the list.
Step 3: Create a Detailed Roadmap
Turn gap analysis into an operational project plan.
- Define Objectives and Scope: For example, “Get GDPR compliance for our main application by the end of the fourth quarter.”
- Break Down the Work: Divide your project into stages or smaller stages, such as “Implementing Access Control Policy” or “Developing an Incident Response Plan”.
- Assign Tasks and Owners: For each stage, define the specific technical tasks required. Assign each task to a team member to ensure clear responsibility.
- Estimate Timelines and Resources: Set realistic deadlines for each task and milestone. Identify the budget, tools and personnel needed to complete the work.
Step 4: Implementation of controls and policy development
Here you put your plan into action.
- Implement Technical Controls: Your engineering team can start implementing the necessary technical safeguards identified in the roadmap.
- Develop Formal Policies: Create and document clear policies and procedures. These should cover topics such as data protection, access control and incident response.
- Teach your team: Conduct training sessions to ensure that each employee understands their role in data protection and compliance with company policies.
Step 5: Monitor, Report, and Improve
Compliance is not a unilateral project; it is a continuous process.
- Establish Monitoring: Establish systems for continuous monitoring of controls and real-time detection of potential problems.
- Prepare for Audits: Perform regular internal audits to ensure that your controls work as expected and that you are prepared for an external audit.
- Stay Informed: Create a process to keep up to date with new requirements and adapt your compliance program accordingly.
How the platform helps with compliance
The platform is your dedicated compliance team, providing a hands-on, expert-led service to manage the entire process for you.
A Truly Tailored Program
We do not use generic templates. We start by talking to you to understand exactly how your business and technology works.Based on this conversation, we build your compliance program from scratch.
- Context-Driven Documents: We create the right documents (policy, inventory and risk analysis) that fit perfectly with the way you work.
- Relevant Checklists: You’ll get a practical, customized checklist of security controls that are needed for your specific operations, not a list of generic, irrelevant tasks.
Expert-Led, “Done-For-You” Service
We deal with the heavy lifting of compliance so you can focus on building your product. in-house compliance experts.
- Noi facem lucrarea: We manage document creation, sampling and even managing relationships with auditors on your behalf.
- Full Lifecycle Support: From the initial conversation to preparing for the audit and keeping your compliance in the background, we are with you at every step.
Complete Transparency and Ownership Our approach is based on trust and transparency, ensuring you always have control.
- Open-Source Foundation: As a platform, we offer complete transparency, without blocking the provider.
- You own the data: Always hold your documents and compliance data, giving you full control and peace of mind.
Conclusion
Navigating on the path to compliance is an essential step for any ready-to-scale start-up. While a structured roadmap provides the necessary steps, the journey can be complex and rich in resources when managed on its own. This is exactly where the platform enters. Our hands-on, expert-led service is designed to manage the entire process for you from creating a customized program that fits the way you work to managing auditors on your behalf. By partnering with the platform, you turn compliance from a frightening obstacle to a strategic asset, building the foundation of trust and security you need to complete larger transactions and grow with confidence.