





June 19, 2026
IAM
Personal API Tokens
Create, list and revoke your own carrier tokens for scripting against ZebraByteAPI, without sharing a service account with your team.
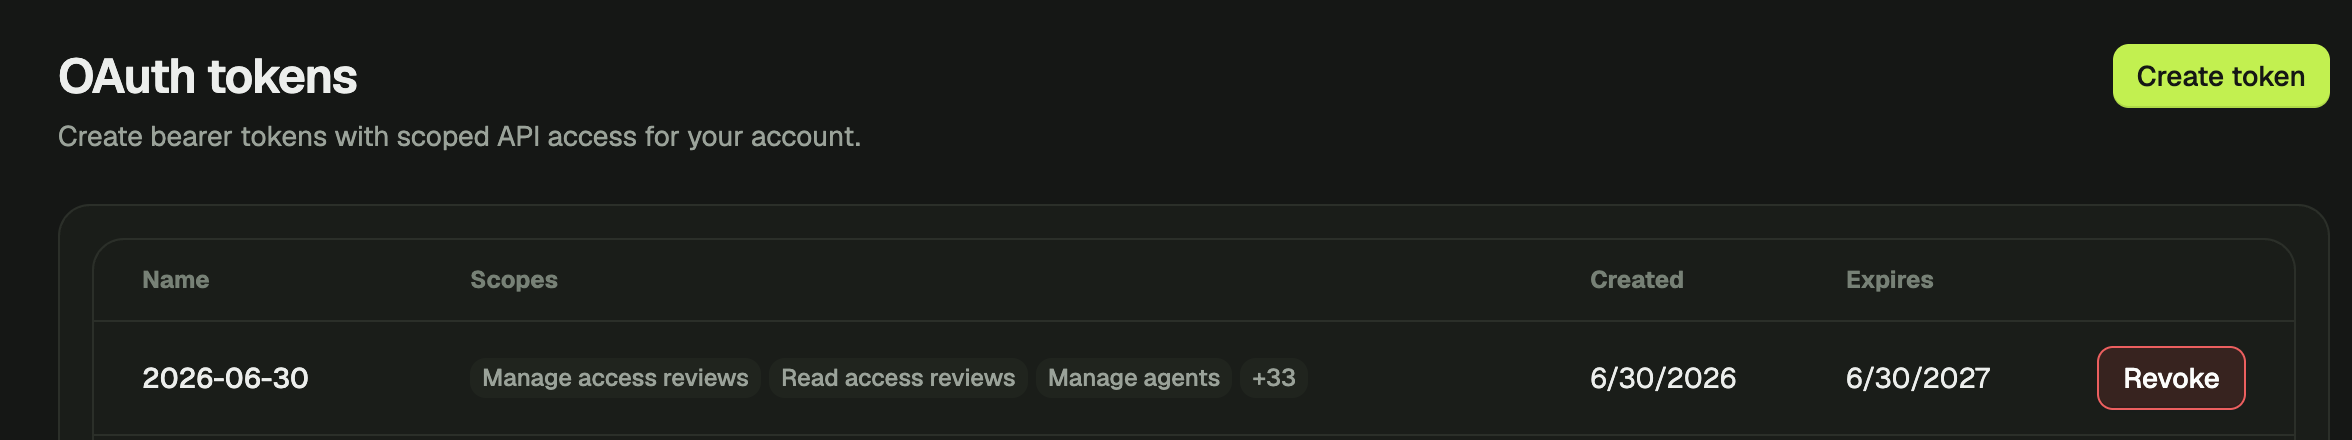
So far, calling ZebraByteAPI out of the console has meant either building an OAuth2 application, or borrowing a token for something else.
Personal TokensAPI solve this. Go to /me/oauth-tokens in the console and you can create a carrier token covered by your identity, list the tokens you have issued and revoke them on site. Each v1API application domain is now registered and applied, so the tokens only work for what they have been granted.
Auditors are given the v1:iam:read scope by default, which covers access only for reading to most auditing tools needs without a separate application.
