How long does it take to be ISO27001 certified?
Even for small companies, achieving ISO 27001 certification This guide breaks down your calendar into clear phases so you know exactly what to expect.
Key Takeaways
- Expect a 3 to 8-month journey: For most small and medium-sized enterprises, the entire ISO27001 certification process from start to finish takes about 3 to 8 months.
- Size and complexity matter: The time may be shorter (2-4 months) for very small, agile start-ups with a simple technology stack, but extends beyond a year for larger or more complex organizations.
- It’s a phased project: The process is not a single sprint. it is a structured project with distinct phases toward compliancecoverage, risk assessment, implementation and final audits.
Breaking down the ISO 27001 timeline
The path to ISO27001 certification is a marathon, not a sprint.
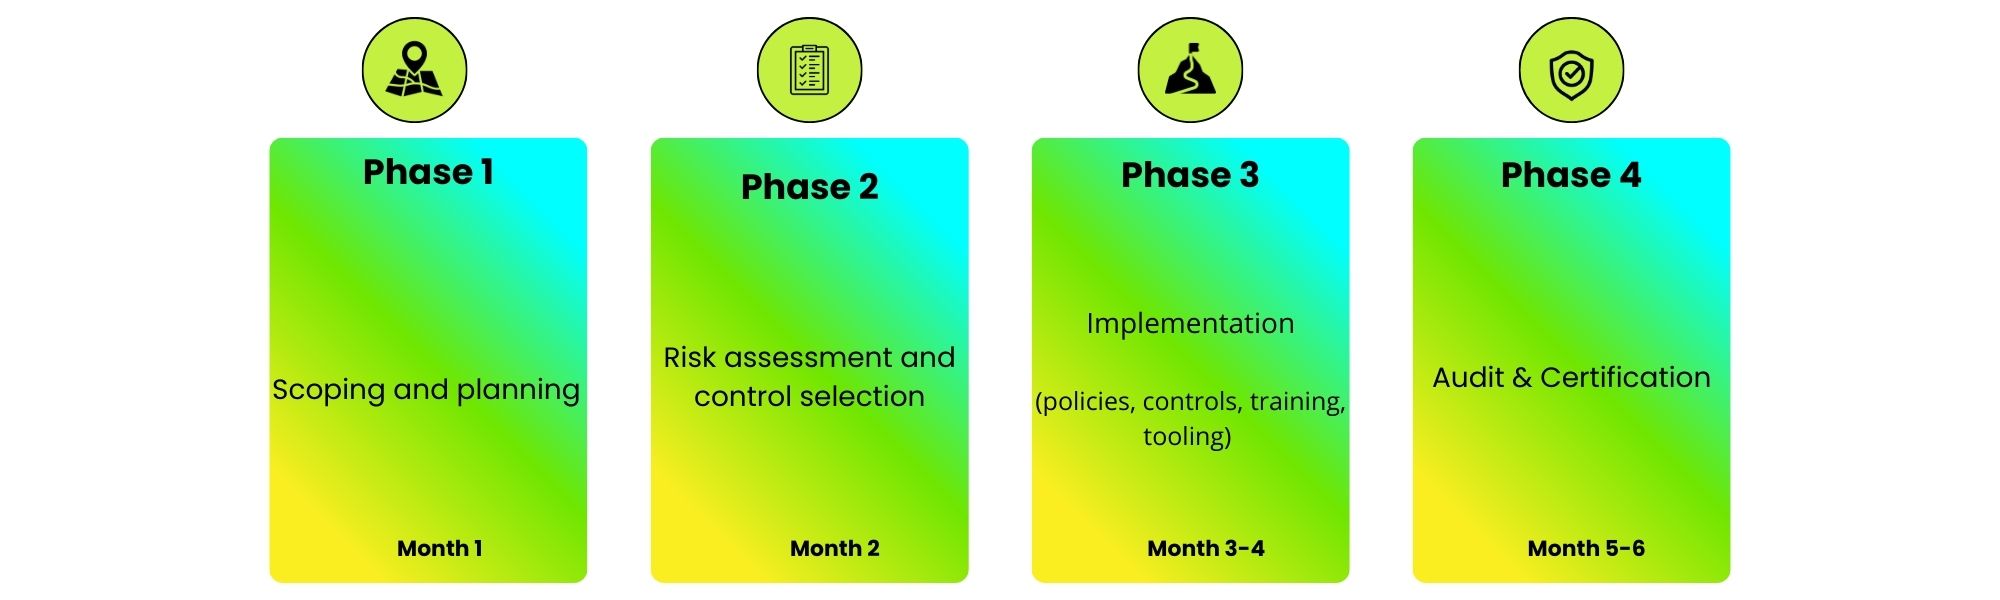
Phase 1: Scoping and planning (month 1)
This is the basic stage in which you define the scope of the Information Security Management System (ISMS). You will decide which parts of your business, which products and which offices will be covered by certification.
Stage 2: Risk assessment and control selection (month 1)
This is the essence of the ISO27001 process. Your team will conduct a formal risk assessment to identify threats and vulnerabilities to your information assets. Based on this assessment, you will select the appropriate security controls from Annex A to ISO27001 to mitigate these risks.
Phase 3: Implementation (month 2-4)
This is often the longest and most resource-consuming phase. Here you implement your selected controls and policies. This involves everything from writing new security policies and training your staff to implementing technical controls such as access management and data encryption. penetration test at this stage to validate their technical controls.
Phase 4: Audits and certification (months 5-6)
Once your ISMS is fully deployed and has been in operation for a period, you can start auditing:
- Internal Audit: The auditor checks whether the ISMS documentation is properly designed, implemented andined in practice.
- Certification audit:
- Step 1 Audit: The auditor reviews your documentation to ensure that the ISMS is properly designed.
- Step 2: The auditor performs a deeper immersion, reviewing the evidence and interviewing your team to ensure that your ISMS is fully and effectively implemented.
Typically, people keep at least 15 days between Stage 1 and Stage 2 to solve potential problems raised by their auditor.
How the Timeline Platform Accelerates ISO27001
The traditional 3 to 8 month timeline is a significant commitment that leaks out the most valuable resources of a start-up: time and engineering. the platform was built to remedy this. we act as an internal compliance officer would.
- We do the heavy lift for you: We deal with the most complex parts, such as conducting formal risk assessment, selecting the right controls, and creating all necessary documents (policy, procedures) tailored to your business.
- We release our engineers: The implementation phase can distract your technical team from their basic tasks. We provide your team with a practical, prioritized checklist of only the necessary and relevant security controls. This means that they can focus on building your product, not on becoming experts in compliance.
- Managing the audit work: Our expert team acts as your dedicated compliance team during the audit process. We prepare evidence, manage communications with the auditor and ensure that the entire process runs smoothly and efficiently.
Conclusion
The traditional 3- to 8-month path to certification ISO27001 is a major block for start-ups trying to move quickly and win customers worldwide. This is the problem that the platform’s expert-led “do-for-you” service was built to solve. We replace the long and manual process with a quick and customized schedule, managing everything from risk assessment to final audit management. We save you hundreds of hours and allow you to build trust with international customers faster.
Frequently asked questions
Can we get the ISO27001 certification in less than 6 months?
It’s possible for small with a simple set of technologies and some existing security controls, but it’s an ambitious timeline.
What is the most difficult part of the ISO27001 process?
For most start-ups, the risk assessment and implementation stages (phase 2 and 3) are the most challenging.Risk assessment requires a specific methodology that may be unknown, and implementing dozens of new policies and controls can be a heavy lift for a small team.
Do we need a dedicated person to manage the ISO27001 project?
Yes, you’ll need a dedicated project leader. However, this person doesn’t have to be a full-time compliance expert. In small companies, it’s usually the executive director or CTO. Many start-ups have found success by partnering with a compliance team like us, who acts as your dedicated compliance team, managing the project during implementation, streamlining auditing and running ISMS documentation for you. Lucis achieved their ISO 27001 certification With this approach.
What happens after obtaining the certification?
After initial certification, you will have annual supervisory audits to ensure that you continuously maintain and improve your ISMS.