





Tailscale
Connect Tailscale as an access review source using an access token so that the platform can list each user of your tailnet and their assigned role.
The platform reads Tailscale tailnet users through TailscaleAPI so you can check who has access.
Prerequisites
Section entitled ‘Prerequisites’- the platform organization administrator access
- The Owner, Admin, IT admin, or Network admin role in Tailscale (only these roles can generate an access token)
- A Tailscale account that can read tailnet users because an access token has the same permissions as the user who created it
Collected Fields
Section entitled “Collected Fields”| the platform field | Tailscale field | Notes |
|---|---|---|
| Name | displayName |
The left is empty when Tailscale does not have a display name for the user |
loginName |
Tailscale calls it login name. A user without one is omitted | |
| Role | role |
One role per user: owner, admin, it-admin, network-admin, billing-admin, auditor, or member |
| Admin | role |
Register as an administrator when role is owner, admin, it-admin, network-admin, or billing-admin |
| Status | status |
active and idle are listed as assets, suspended as inactive. needs-approval and over-billing-limit leave the state unknown |
| MFA | Not supported | |
| Last login | lastSeen |
The last time one of the user’s devices logged in and the last time the user logged in to a Tailscale service |
| External ID | id |
Stable ID used to track your account through reviews |
| Created at | created |
When the user joins the tailnet |
Tailscale delegates authentication to the identity provider or passkey with which each user logs in, and its users do not return any MFA fields.
Step 1: Create an API Access Token
Section entitled “Step 1: Create anAPIAccess Token”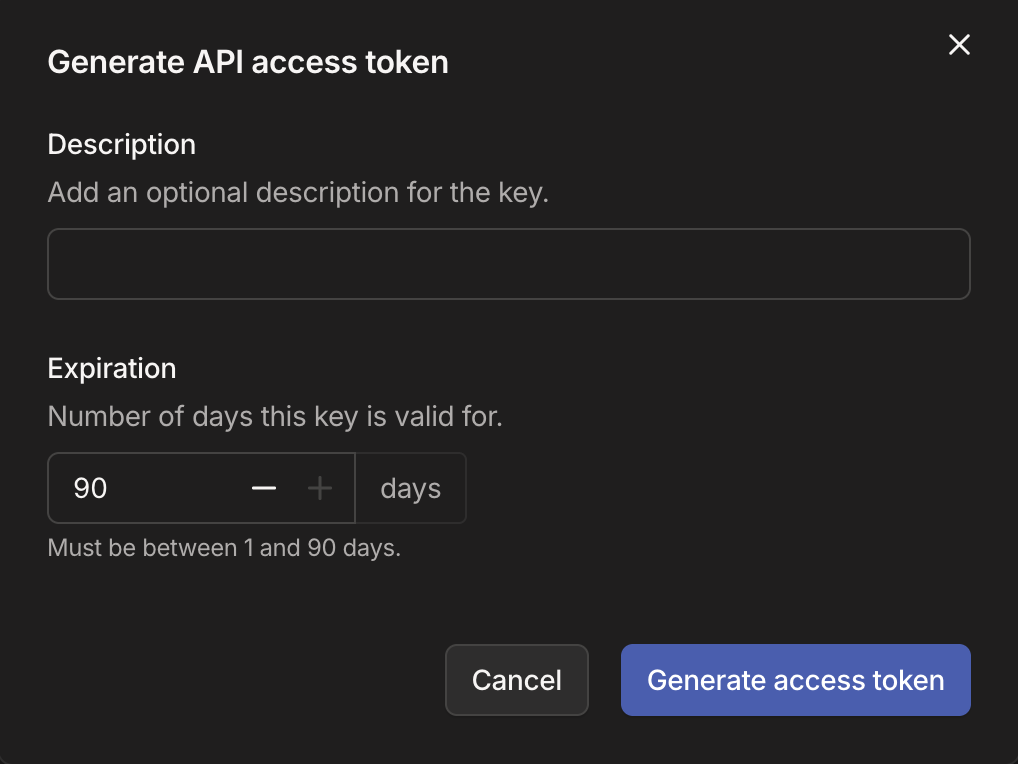
- In the Tailscale administration console, recorded as Owner, Admin, IT admin, or Network admin, open the Keys pagina şi du-te la API access tokens section.
- Select Generate access token, add a Description (e.g.
Probo Access Review) and set ExpirationTailscale allows between 1 and 90 days. - Copy the token (
tskey-api-…) and store it securely. Tailscale displays a complete secret once.
Step 2: Connect in the platform
“Step 2: Connect in the platform”- On the platform, go to Access Reviews > Sources > Add Source.
- Find Tailscale, click API Key, attach the access token and click Connect.
This name is just a platform tag, so it can differ from how Tailscale identifies tailnet.
Troubleshooting
Section “Troubleshooting”- Token rejected. Confirms that it is an access tokenAPI(
tskey-api-…). No auth key (tskey-auth-…) no secret OAuth client (tskey-client-…) authenticates a TailscaleAPI request. - Source stops synchronization after a few weeks. A Tailscale access token expires after 1 to 90 days chosen when it was generated.
- No members appear. An access token has the same permissions as the user who created it, and the user’s endpoint returns 404 when that user can’t read tailnet users.
- A user shared on another tailnet is missing. Endpoint users return tailnet members by default, so the platform does not import shared users from elsewhere.